
In This Article
Your board asked whether the company “has AI governance,” and when you looked around the room, nobody agreed on what the question even meant.
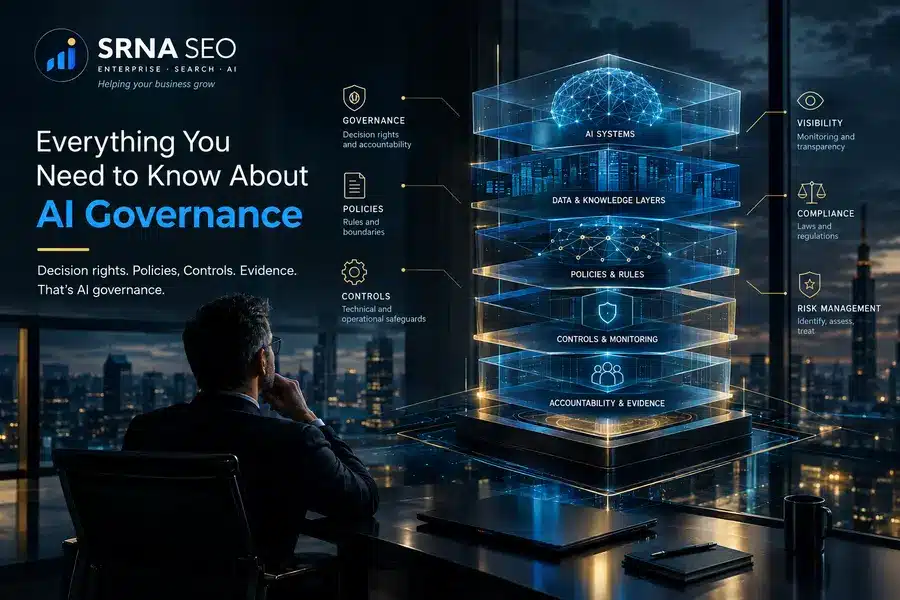
AI governance is the set of decision rights, policies, controls and evidence that decide who may do what with AI inside your organization, and who answers when it goes wrong. That is the whole thing. Frameworks, laws, committees and software are machinery that serves that one sentence. If you cannot say who approved a given AI system, what it is allowed to touch, and how you would find out if it started misbehaving, you do not have AI governance. You have AI usage.
This is the long version. I wrote it for SEO managers, heads of digital, VPs and C-suite people who keep hearing the term in meetings and still cannot get a straight answer. I spent seven years inside global enterprises before I started advising independently, so I will try to give you the in-house view, not the textbook one. And yes, I have opinions. Some of them are uneven.
What AI Governance Actually Is
Take the definition apart.
Decision rights means a named person or body can say yes or no to an AI use case, and that authority is written down.
Policies are the rules those people apply (what data may go into a model, which use cases are banned, when a human must review the output).
Controls are the mechanisms that make the rules real: access limits, testing, approval gates, logging.
Evidence is the proof, kept somewhere an auditor, a regulator or your own board can look at it later.
Gartner frames it in similar terms, as assigning accountability and decision rights for AI and then assuring those rights are followed. The ISO and NIST material says roughly the same thing with more paperwork.
One thing the definitions often skip: governance covers the whole life of a system. Idea, procurement or build, testing, deployment, monitoring, change, retirement. A policy that only exists at the approval stage is a gate, not governance. The system you approved in March is not the system running in October (models get updated, data drifts, someone connects a new tool to it).
How AI governance differs from the things it gets confused with
| Term | What it covers | Where it stops |
|---|---|---|
| Data governance | Data ownership, quality, access, lineage | Does not decide whether an AI use case should exist |
| AI ethics | Values and principles (fairness, transparency, human dignity) | Principles without owners and controls change nothing |
| AI risk management | Identifying, scoring and treating specific AI risks | One function inside governance, not the whole thing |
| Compliance | Meeting legal and contractual requirements | Legal minimum, not the same as being well run |
| AI governance | All of the above, tied together with accountability and evidence | Does not build or tune the models themselves |
The practical consequence: if you already have a data governance team, a privacy office and a security function, you are not starting from zero. You are starting with three groups who each own a slice and have never been put in the same room about AI.
What AI Governance Is NOT
I will be blunt, because this is where executives waste the most money. It is not a policy PDF. A document that nobody can enforce is a liability, because it proves you knew what to do and did not do it.
It is not a committee. I have seen “AI councils” that meet monthly, approve nothing, block nothing, and produce minutes. A committee is a place where governance can happen. It is not governance by itself.
It is not a tool you buy. Software helps with inventory, workflows and monitoring, but no platform decides who is accountable inside your company. Only your executives can do that.
It is not only about stopping things. Good governance makes approval fast for low-risk use cases so people stop hiding their AI use from you. And it is not the same as an AI strategy. Strategy says where you want to use AI. Governance says under what conditions.
Governance that only says no gets routed around, and routed-around governance is worse than none, because it gives leadership a false picture.
Why This Became Urgent
Three things changed at once.
First, regulation stopped being theoretical. The EU AI Act (Regulation (EU) 2024/1689, the European Union’s binding horizontal law on AI) entered into force on 1 August 2024 and is applying in phases. More on its current timeline below.
Second, AI moved from answering questions to taking actions. An AI agent (a system that can use tools, call other systems and complete multi-step tasks with limited human input) is not a chatbot. It can change a record, send a message, or approve something. I covered the architecture side in AI Agents: Architecture, Autonomy and Governance.
Third, employees adopted AI faster than any policy could follow. People paste contracts, customer data and strategy decks into tools that IT never reviewed. I do not have a clean cross-industry number for how widespread this is, so: Not enough available data for a figure I would stand behind. But ask any CISO whether it happens in their company and watch their face.
What Is Inside a Working AI Governance Program
Strip away the vendor decks and a working program has six parts. Not twenty. Six.
1. An inventory of every AI system
You cannot govern what you cannot list. The inventory covers systems you built, systems you bought, AI features embedded in software you already pay for, and the unofficial tools people use on their own. For each one: a business owner, a purpose, the data it touches, the vendor, and a risk tier.
This is the unglamorous part and it is where most programs stall. Most organizations do not have an AI governance problem. They have an AI inventory problem. Until the list exists, every other conversation is guessing.
2. Named accountability
Every AI system needs one accountable business owner, not a department. Above that you need an executive sponsor with budget, and a governance lead who runs the process day to day. Legal, privacy, security and the relevant business unit all have seats, but one person answers for each system.
I wrote about the accountability question from the outside-facing angle in AI Accountability: Who Is Responsible for an AI’s Representation. The short version is that “everyone” is the same as “no one.”
3. Policy and risk classification
You need a small set of rules people can actually read. Which use cases are prohibited. Which are allowed with review. Which are allowed freely. What data may enter which systems. When a human must check the output before it goes anywhere.
Risk tiering is the engine here. A tool that drafts internal meeting notes and a model that screens job applicants should not go through the same process. If they do, either the first one is slowed to a crawl or the second one is under-reviewed. The EU AI Act uses the same logic (tiers of risk with obligations scaled to match), and it is a sensible template even if you are not in scope.
4. Controls across the lifecycle
Controls are the part that makes policy bite. Before deployment: testing for accuracy, bias and security, a documented purpose, a data check, an approval record. During operation: access limits, logging, human oversight where required, a way for users to report problems. After: monitoring for drift and incidents, a change process, and a retirement process.
For agents add one more layer, permissions. What can this agent read, what can it write, what can it trigger, and who can switch it off. If you have agents in production and have not asked those four questions, start there. I laid out how to do that in How to Audit an AI Agent.
5. Evidence and monitoring
If it is not recorded, it did not happen. Auditors, regulators and enterprise customers will ask for evidence: the inventory, the risk assessments, approval records, test results, incident logs, training records. Monitoring closes the loop. It tells you whether the controls are working or just exist.
6. Literacy and culture
People who do not understand what AI can and cannot do will either overtrust it or hide it. Training is a control. The EU AI Act includes AI literacy obligations for organizations (applying since February 2025), and beyond the legal angle, adoption without understanding is just exposure. I wrote the framework for this in The AI Literacy Framework.
Where Are You Starting From?
Before you build anything, measure the gap. If you want a quick, structured read on where your organization stands, the Free Assessment Center on this site is built for exactly that first look. And if your question is more about what AI systems can learn and repeat about your organization, start with the Knowledge Exposure Audit (an audit of what AI systems can pick up and say about you, which your regular security audit never asks).
For a broader readiness view, my guide on how to evaluate an organization’s AI readiness walks through the same ground in more depth.
The Frameworks and Laws That Matter
There are four reference points you will hear in every serious conversation. They are not interchangeable.
| EU AI Act | NIST AI RMF 1.0 | ISO/IEC 42001:2023 | OECD AI Principles | |
|---|---|---|---|---|
| Type | Law (Regulation (EU) 2024/1689) | Voluntary framework from the US National Institute of Standards and Technology, published January 2023 | International management system standard, published December 2023 | Intergovernmental principles, updated May 2024 |
| Binding? | Yes, with fines | No | No (voluntary) | No |
| Certifiable? | No (high-risk systems go through conformity assessment) | No | Yes, by external audit | No |
| Best used for | Knowing what you must do if you operate in or sell into the EU | Structuring AI risk work, especially as an entry point | Proving a working governance system to customers and regulators | Shared vocabulary and policy direction |
The EU AI Act, and the date everyone gets wrong
The dates changed this year, and a lot of explainers still show the old calendar. As I write this in October 2026, here is the picture, based on current legal commentary (check with your counsel before relying on it, I am not a lawyer):
- The Act entered into force on 1 August 2024.
- Prohibited practices and AI literacy obligations applied from February 2025. General-purpose AI model obligations started applying from August 2025.
- The Digital Omnibus on AI, Regulation (EU) 2026/1744, entered into force on 27 July 2026. It moved the deadline for stand-alone high-risk systems (Annex III: recruitment, credit scoring, education, law enforcement, border control and similar) from 2 August 2026 to 2 December 2027.
- High-risk AI embedded in regulated products (Annex I: medical devices, machinery and similar) moved to 2 August 2028.
- Article 50 transparency duties (telling people they are dealing with an AI, marking AI-generated content) were not postponed. Commentary points to a short grace period for watermarking on systems already on the market, ending 2 December 2026.
So the heavy conformity work got more time. The transparency and literacy work did not. And penalties are not small: for prohibited practices, the Act allows fines of up to 35 million euros or 7% of worldwide annual turnover, whichever is higher.
My honest view: treating the postponement as a pause is a mistake. The delay was granted because supporting standards and guidance were late, not because the obligations got lighter. Organizations that use the extra months to build the inventory and the risk tiers will be calm in 2027. The others will be doing it under deadline pressure with outside lawyers billing by the hour.
NIST AI RMF versus ISO/IEC 42001
People ask me which one to pick. Wrong question, usually.
The NIST AI Risk Management Framework is built around four functions: Govern, Map, Measure and Manage. It is free, flexible, not certifiable, and good at giving a team a shared language for AI risk. ISO/IEC 42001 is a standard for an AI management system (AIMS), meaning a formal, auditable way of running AI governance with defined roles, records and continual review. It was designed to sit next to ISO standards you may already hold, such as ISO 27001 for security.
My rule of thumb: start with NIST if you are building from scratch and need to get moving. Move to ISO 42001 when customers, regulators or procurement start asking for independent proof. Many organizations end up using both, NIST for how they think about risk and ISO for how they prove it. Neither makes you compliant with the EU AI Act by itself, though both produce documentation that helps.
Governing AI Agents: The Part That Changes the Rules
Classic governance assumed a human reads the output and decides. Agents break that assumption. When a system acts on its own, a bad answer becomes a bad action, and the time between the two can be seconds.
Four questions cover most of the exposure. What can the agent access? What can it change? Who can stop it, and how fast? What gets logged so you can reconstruct what happened? If any answer is “we are not sure,” that agent is running outside governance whatever the policy says.
If you want a structured way to check this, the Agent Exposure Audit (an audit of how exposed your AI agents are to misuse and over-reach) is one place to begin. The longer reasoning on autonomy levels is in the agents governance piece I linked above.
The Half of AI Governance Almost Nobody Covers
Most guides stop at internal AI use. Models you build, tools you buy, rules for staff. That is half the problem.
The other half is how external AI systems (ChatGPT, Gemini, Copilot, Perplexity and the rest) describe your organization to the people who matter: buyers, candidates, journalists, regulators. That representation is built from whatever those systems can find about you. If your public information is inconsistent, outdated or thin, the AI fills the gaps, and sometimes it gets them wrong.
Nobody in most companies owns this. Marketing assumes it is an SEO thing. Legal assumes it is someone else’s. Security never considered it. I wrote about the risk side in AI Misrepresentation Risk and about whether you can do anything about it in AI Correction Rights. The honest answer on correction is “partly, and slowly,” which is exactly why governance has to be proactive.
This is where my own work sits. I built the AI Visibility Governance Blueprint to give enterprises a way to assign ownership and monitoring for how AI represents them. For measurement, there is NovaX (my AI visibility intelligence platform) and the AI Visibility Inspector (a diagnostic that checks how AI systems see a website). They sit inside the monitoring layer of the program described above, not outside it.
If an AI system is telling your future customers something false about you, and nobody in your company is accountable for noticing, that is a governance failure, not a marketing glitch.
Who Owns AI Governance Inside the Company
There is no single right org chart. But here is the split that I see working in large organizations, and I say that as someone who has watched the opposite fail.
| Role | Owns |
|---|---|
| Executive sponsor (C-suite) | Budget, risk appetite, final escalation |
| AI governance lead | The process, the inventory, the calendar, the reporting |
| Business owner per AI system | Purpose, outcomes, day-to-day accountability |
| Legal and privacy (including the DPO where one exists) | Regulatory interpretation, data protection impact |
| Security | Access, threat modeling, incident response |
| Digital, SEO or communications lead | How external AI systems represent the organization |
The last row is the one that gets left off. Add it.
A 90-Day Starting Plan
Not a perfect plan. A plan that gets you from nothing to something defensible.
- Days 1 to 15: Name the sponsor and the lead. Without these two, nothing else matters. Get written agreement on who they are.
- Days 1 to 30: Build the first inventory. Spreadsheet is fine. Survey every department, check procurement and software spend, and include shadow tools. Expect to be surprised.
- Days 15 to 45: Draft a risk tiering model. Three tiers are enough to start. Decide which use cases are banned outright.
- Days 30 to 60: Write the short policy set. Acceptable use, data handling, human review rules. Keep it readable. If staff need a lawyer to understand it, it will be ignored.
- Days 45 to 75: Run your highest-risk systems through review. Document owner, purpose, data, testing, oversight, monitoring. This produces your first real evidence.
- Days 60 to 90: Start training and reporting. Basic literacy for everyone, deeper training for owners, and a one-page quarterly report to the executive sponsor.
- Day 90: Decide on frameworks. Map what you built to NIST AI RMF, and decide whether ISO/IEC 42001 certification is worth the cost for your customers and sector.
If your organization is large, global or heavily regulated, 90 days will cover the foundation, not the finish. That is fine. Finish is not the goal. A running system is.
Where Programs Fail
- Starting with tools. Buying a platform before the inventory and ownership exist.
- Governance by committee. Lots of meetings, no decision rights.
- One-size-fits-all review. Everything treated as high risk, so people avoid the process.
- No evidence trail. Decisions made but never recorded.
- Ignoring external representation. Governing what you use but not what AI says about you.
- Treating the EU AI Act delay as relief. Transparency and literacy duties are already live.
What You Can Honestly Expect After Implementation
I will not give you a made-up percentage. Not enough available data to publish an improvement figure that holds across industries, and anyone promising one is selling something.
What I can tell you is what to measure, so you build your own numbers. Track the share of AI systems in the inventory that have a named owner and a risk tier (this should climb from unknown to close to complete). Track average time from AI request to decision for low-risk cases (it should fall as the tiering matures). Track the number of AI incidents found by your own monitoring versus found by someone outside (the ratio should shift toward your own). [AUTHOR CHECK: if you have real figures from client or in-house work, add them here as a range, otherwise leave this section as written.]
Final Word
AI governance is not a mystery and it is not a one-time project. It is a set of named people, written rules, working controls and kept records, applied across the life of every AI system you run, and extended to how outside AI systems describe you.
Start with the list of what you actually have. Name who answers for each item. Everything else grows from there.
If you want a second pair of eyes on where your organization stands, get in touch or look at how I work in Enterprise Search Advisory. I advise SEO managers, heads of digital and executive teams who need a clear answer, not another framework deck.
Frequently Asked Questions
It is the set of decision rights, policies, controls and evidence that determine who may do what with AI inside an organization and who is accountable when something goes wrong.
No. Ethics sets the values (fairness, transparency). Governance gives those values owners, rules and controls. Principles without owners change nothing.
Data governance covers ownership, quality, access and lineage of data. AI governance sits across it and adds decisions about whether an AI use case should exist at all, how it is tested, and how it is monitored over its life.
One executive sponsor, one governance lead, and one accountable business owner per AI system, supported by legal, privacy and security. A committee alone is not enough. I also recommend adding the digital or SEO lead for external AI representation.
NIST AI RMF is free, flexible and not certifiable, so it works well as a starting point. ISO/IEC 42001 is certifiable and useful when customers or regulators want independent proof. Many organizations use both. Neither alone makes you compliant with the EU AI Act.
After the Digital Omnibus on AI (Regulation (EU) 2026/1744, in force since 27 July 2026), stand-alone Annex III high-risk systems apply from 2 December 2027 and Annex I embedded systems from 2 August 2028. Check with legal counsel before relying on dates.
No. It postponed high-risk obligations. Article 50 transparency duties were not postponed, and AI literacy obligations have applied since February 2025.
Build an inventory of every AI system in use, including tools staff use on their own, and assign an accountable owner and risk tier to each.
Because external AI systems build their answers about you from whatever they can find. If nobody is accountable for noticing and correcting wrong information, the organization carries the risk without knowing it.
Governance that only blocks gets bypassed. Risk tiering lets low-risk use cases move fast while higher-risk ones get deeper review, which is how governance supports adoption instead of stopping it.
This article was researched and drafted with the assistance of AI tools and reviewed and edited by author prior to publication.
